Blog
NebulaDNS Complete Feature Guide: k3s, Route53, Observability, and Enterprise DNS
Every “battery included” feature, integrations, and enterprise DNS posture
On this page
Sources
This guide synthesises the public NebulaDNS site and repository github.com/bwalia/nebuladns. Milestones and GA items evolve—verify release notes for your version.
Architecture at a glance
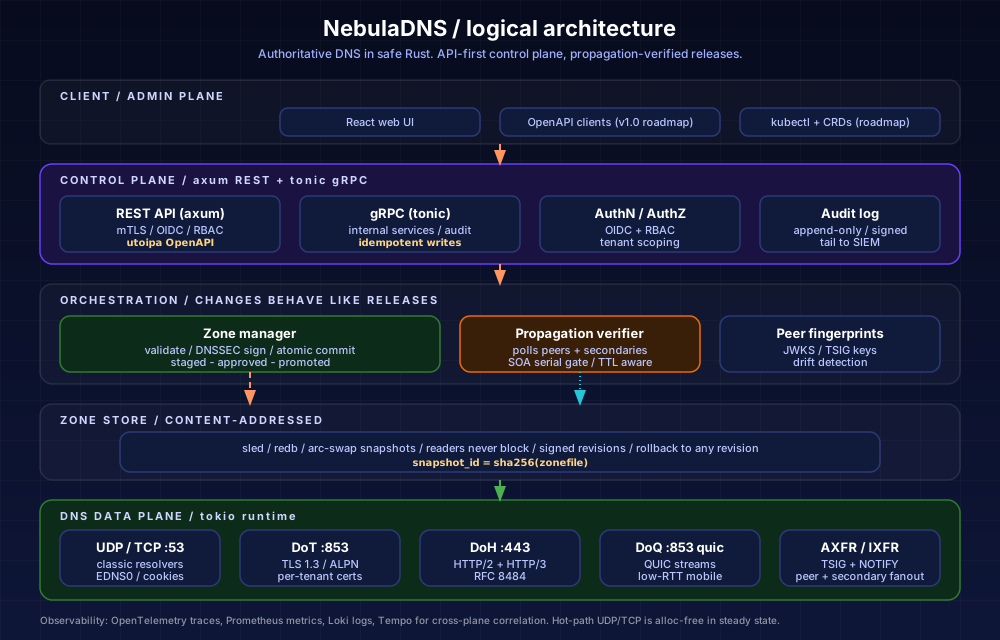
The stack separates control plane (REST/gRPC, authn/z), zone management (validation, DNSSEC signing, atomic commits), propagation verification (secondaries report SOA), content-addressed zone store, and the DNS data plane (UDP/TCP/DoT/DoH/DoQ, transfers, DNSSEC online signer).
Feature catalogue (“batteries included”)
The project markets twelve headline capabilities—summarised here from the landing page.
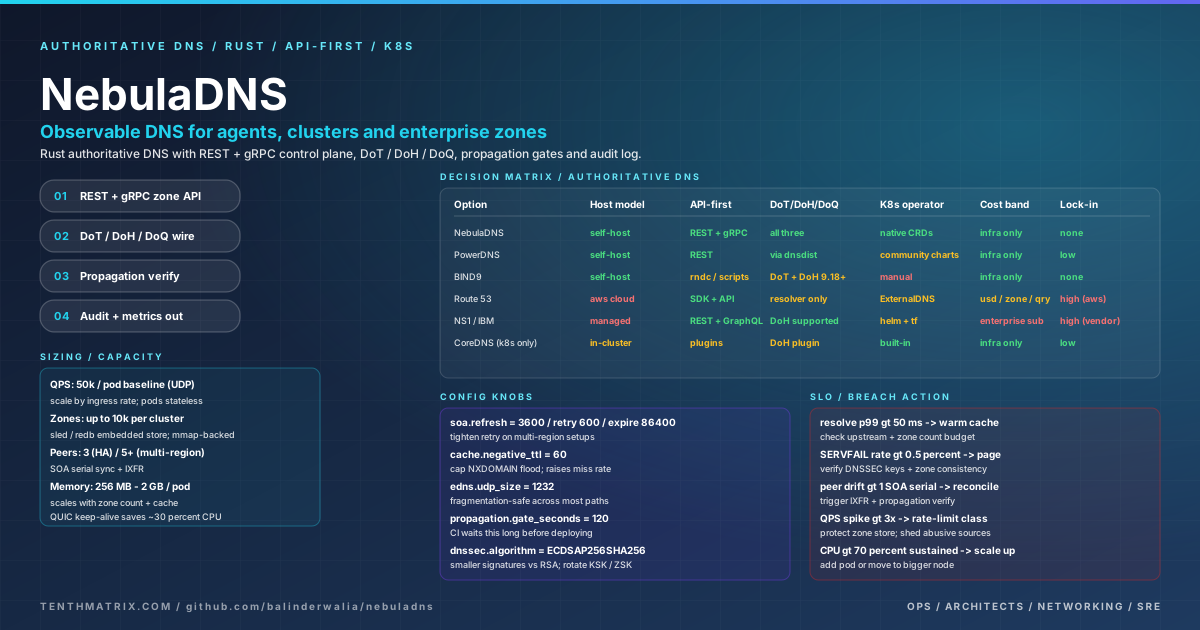
- API-first: REST/gRPC for zones, records, TSIG rotation, rollback—CLI/UI as thin clients.
- Observable by default: Prometheus
/metrics, enum-typed labels, JSON logs, OTLP traces. - Verified propagation: Deploy completes only when declared secondaries acknowledge the new SOA serial.
- Peer software fingerprinting: Records
version.bindCHAOS-style signals so silent BIND upgrades cannot erode redundancy invisibly. - Safe Rust: No
unsafe; continuous fuzzing on codec, parser, DNSSEC signer. - Zero-GC tail latency: Deterministic allocation; lock-free zone snapshots via
arc-swap. - Atomic versioned configuration: Content-addressed zones; roll forward/rollback without partial reads.
- Deterministic SOA serials: Monotonic serial strategy to avoid wedged recoveries.
- Kubernetes-native: Helm chart, operator, CRDs (
Zone,Record,Secondary,TsigKey,DeployGate); GitOps-friendly; CoreDNS cluster-DNS replacement path on roadmap. - Standards-conformant wire: Strict RFC coverage; explicit error types (e.g.
QdCountMismatch). - Redundancy you can see: Dashboard intent for transfer visibility across zones.
- Hardened defaults: systemd hardening, seccomp, non-root containers, small distroless images.
Comparison positioning (high level)
The site publishes a competitive matrix (TinyDNS, BIND 9, Knot, NSD, PowerDNS, CoreDNS, NebulaDNS). Differentiators called out include full REST API, always-on Prometheus, built-in propagation gate, Kubernetes operator + CRDs, peer fingerprinting, and memory-safe implementation. Use the upstream matrix for version-specific claims.
Metrics catalogue (sample)
Examples from the site include query counters, latency histograms, FORMERR tracking, AXFR attempts, per-peer last-success timestamps, propagation lag, and build info. Treat names as illustrative until you scrape a running build.
nebula_dns_queries_total{proto,qtype,rcode}
nebula_dns_query_duration_seconds_bucket{proto,qtype,le}
nebula_axfr_attempts_total{peer,zone,direction,result}
nebula_peer_version_info{peer,software,version}
nebula_zone_propagation_converged{zone}
k3s, CoreDNS, and AWS Route 53
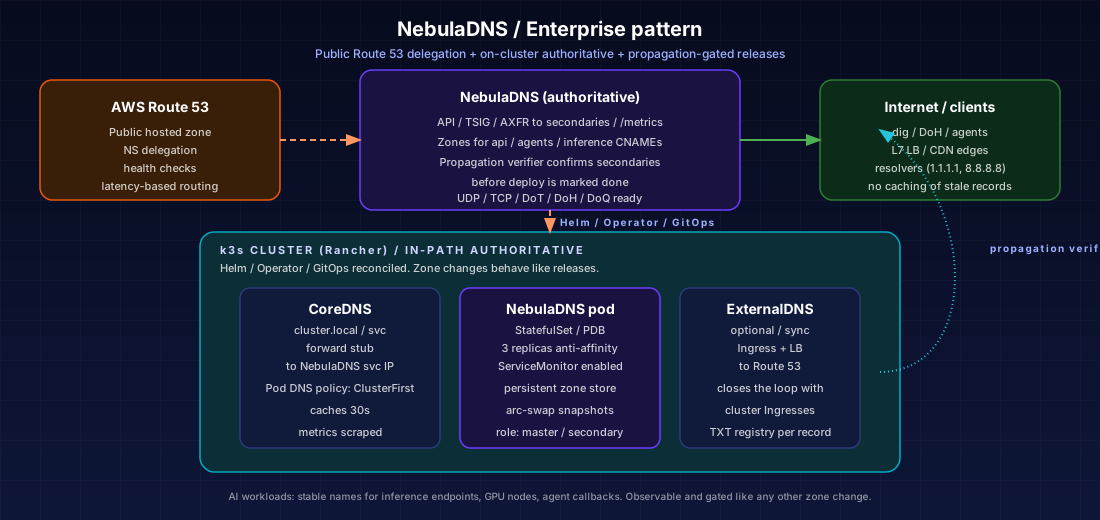
- Route 53: Keep public delegation and health checks in AWS; point NS records at NebulaDNS secondaries or run split-horizon patterns that match your security model.
- k3s / RKE2: Deploy NebulaDNS via Helm with PDB + ServiceMonitor; align CoreDNS forward/stub to NebulaDNS for zones you authoritatively serve inside the estate.
- ExternalDNS: Optional bridge from Ingress/LB objects to public records—coordinate with propagation gates so automation cannot mark “done” early.
Roadmap notes
The public roadmap lists milestones through GA (wire/zone completeness, transfers, DNSSEC, propagation verifier, HA/multi-region, operator). Check PROJECT_PROMPT.md and releases in the repo for dates.
Related launch article
For the “why now / AI era” narrative, read NebulaDNS: game changer in the AI era.
How TenthMatrix can help
We help enterprises ship observable DNS and GitOps patterns around authoritative stacks—contact info@tenthmatrix.com.
More from the blog
Observability Is Not Optional: Make It a Business Standard
Why fragmented monitoring creates blind spots, duplicate spend, and slow incidents — and how to make centralised observability a non-negotiable company standard.
WSL Vault for Compliance: One Tenant Never Opens Another’s Secrets
How WSL Vault keeps app, team, and environment tenants cryptographically isolated — so a stolen root-style token cannot empty the estate — and why dual-tenant control beats secrets sprawl.
Workstation AI Shop: Promoting the AI Sales Storefront Through int → test → acc → prod
Workstation AI Shop sells GPU machines with a fully autonomous AI Sales Agent that configures the basket. See how Ring Promoter moves each build through int → test → acc → prod — with Orbit screenshots release engineers and stakeholders share.